Authorization
Most APIs need credentials. The Authorization tab of an endpoint adds them to the request for you, so you don't have to build the Authorization header by hand.
Supported types
DocStar supports three authorization types:
| Type | What DocStar sends |
|---|---|
| No Auth | Nothing. This is the default. |
| Basic Auth | An Authorization: Basic <base64 of username:password> header. |
| OAuth 2.0 | An access token, either as an Authorization header or as an access_token query param. |
For an API key or a static bearer token, add the header yourself in the Headers tab, for example Authorization: Bearer {{token}} or x-api-key: {{apiKey}}. Keep the value in an environment variable so it isn't saved in the endpoint.
Set up Basic Auth
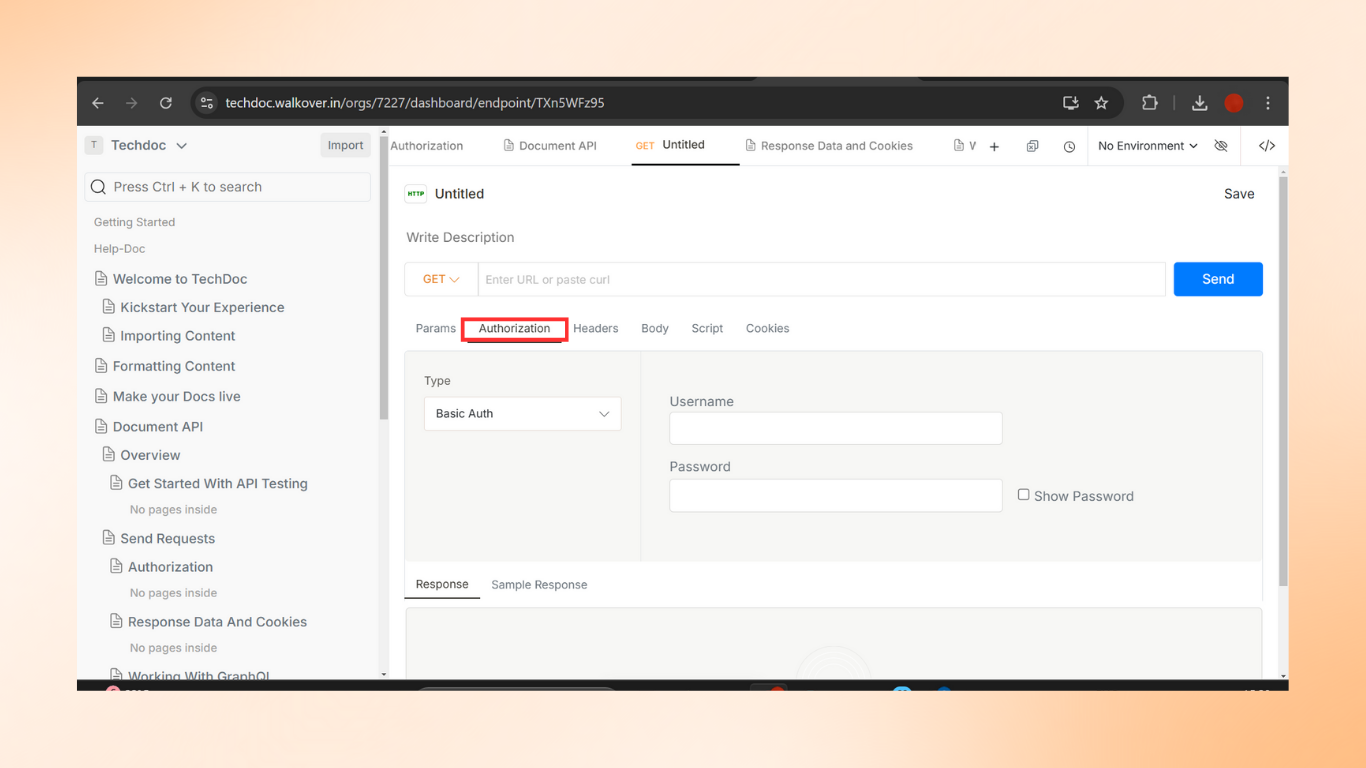
- Open the endpoint and go to the Authorization tab.
- In Type, choose Basic Auth.
- Enter the Username and Password. Tick Show Password to check what you typed.
- Click Send.
DocStar adds the Authorization header to the Headers tab and updates it as you type.
Set up OAuth 2.0
- In the Authorization tab, set Type to OAuth 2.0.
- In Add authorization data to, choose Request Headers or Request URL.
- Paste a token into Access Token, or click Get New Access Token to request one.
- In the Get new access token dialog, enter a Token Name and pick a Grant Type:
- Authorization Code
- Authorization Code (With PKCE)
- Implicit
- Password Credentials
- Client Credentials
- Fill in the fields the grant type needs, such as Callback URL, Auth URL, Access Token URL, Client ID, Client Secret, Scope, State and Refresh Token URL. For PKCE, also set Code Challenge Method and Code Verifier. For Password Credentials, enter Username and Password.
- Under Client Authentication, choose Send as Basic Auth header or Send client credentials in body.
- Click Request Token. Click Save to keep this setup for next time.
For the Authorization Code and Implicit grants, DocStar opens the provider's sign-in page in a pop-up window. After you approve, the token comes back to DocStar. Allow pop-ups for DocStar in your browser.
Manage tokens
Saved tokens appear in the Available Tokens dropdown next to Access Token. Pick one to use it. Choose Manage Tokens to see token details, click Use Token, or delete tokens you no longer need.
If a token has expired, and it has a refresh token and a Refresh Token URL, DocStar refreshes it before sending the request.
Tips
- Changing the type updates the Headers or Params tab. Check there if a request is sending the wrong credentials.
- Before you publish an endpoint, remove real secrets. DocStar warns you if it finds sensitive values when you click Publish.
- Readers of your published docs can supply their own values through a public environment.